PHP Patches Two 9.2-Rated Flaws Today as eMudhra's Weak Keys Force a Web Trust Cleanup
PHP ships an emergency security release today at 14:00 UTC for two vulnerabilities rated CVSSv4 9.2, while Cloudflare deploys mitigations for eight eMudhra certificates whose private keys were reportedly chosen "between 1 and 256." On the AI side, DeepSeek open-sourced its production inference stack under Apache 2.0 and a 163 MB open speech model claimed victory over Whisper.
Quick Hits
- PHP's security team releases fixes for two vulnerabilities rated CVSSv4 9.2 today at 14:00 UTC. @attrc warns of a remotely exploitable flaw in the core engine of all PHP versions, and @mattjay reads the advice to take unpatched apps offline as a measure of how serious this could get.
- Eight eMudhra intermediate certificates used weak keys, and @GergelyOrosz reports the private keys were chosen "between 1 and 256." @Cloudflare says it is deploying mitigations and releasing client updates.
- @superalesha, amplified by @HealthRanger, reports that DeepSeek released its inference system under Apache 2.0, with the creator of QLoRA rating it on par with OpenAI's stack and better than Anthropic's at their scale.
- @marsrepublica's recap of the SpaceX earnings report is packed with claims: Tesla and SpaceX have formed merger committees, $500B-$1T ARR is targeted by end of 2027, and a 440K-GPU Vera Rubin cluster would train Grok by Q2 2027. Single source, unaudited, treat accordingly.
- In home-hardware notes: @Techishala (reshared by @iM4CH3T3) warns some jailbroken PS5s lose fan control and overheat, @thekitze shares a Stremio-plus-Real-Debrid setup that plays everything instantly for 4 EUR a month, and @ScriptedAlchemy compresses the "no Tailscale on the work computer" standoff into two lines.
PHP's Emergency Patch Window Opens at 14:00 UTC Today
The advance notice came from @ThePHPF, quoted by @markgadala: a security release on Wednesday, October 21st at 14:00UTC, covering two critical vulnerabilities both rated CVSSv4 9.2, with an earlier release if details leak or active exploits appear.
@attrc, quoted by @mattjay, says full details of a remotely exploitable vulnerability in the core engine of all PHP versions will be published October 21st, and urges organizations with internet-facing PHP to patch the minute updates land or strongly consider taking applications offline until they can. @mattjay's reaction: "This is gonna be a bloodbath" if Andrew is telling people to take PHP offline preemptively.
@markgadala adds scale, with the numbers attributed to him rather than confirmed: nearly 70% of websites with a known server-side language run PHP, versions dating back to 2004 could be affected, and CERT-EU is warning organizations to patch or pull exposed applications. His sharpest observation is the post-patch dynamic: once fixes go public, attackers reverse-engineer them and race against unpatched servers. WordPress, Magento, and Laravel deployments are the obvious exposure.
eMudhra Chose Private Keys Between 1 and 256
The certificate authority story is the day's second trust emergency, and the detail defies parody. @GergelyOrosz lays it out: eMudhra had two jobs, generate secure 384-bit private keys and store them safely, and instead "chose private keys between 1 and 256 (the numbers!!)." He quotes @LinusMixson's bafflement that this appears to be higher-effort than standard key generation.
@Cloudflare confirmed that eight eMudhra intermediate certificates use weak keys and says it is deploying mitigations and releasing client updates, with a post explaining the impact and what customers and developers should do next.
@BasedTorba claims roughly 70% of the internet was compromised, though the post he quotes from @theSouilos is more precise: an attacker holding these keys could impersonate any website, including banks; Chrome, Firefox, and Apple already block the compromised certificates, but many apps, developer tools, and systems may still trust them. @theSouilos' checklist is worth following: update browsers, OSes, phones, and desktop apps as patches arrive, avoid untrusted Wi-Fi until updated, and ignore any email offering a "certificate fix."
@CDoombeard extends the lesson to hardware: any device no longer receiving updates is a liability, so update everything and retire what cannot be patched. His evidence is @meowkoteeq demonstrating the problem by MITM'ing TLS on an iPod Touch 4 without even installing a CA cert.
DeepSeek Open-Sources an Inference Stack, Underdog Ships a 163 MB Speech Model
Three releases pushed real capability into open licenses today. The biggest is DeepSeek's. Per @superalesha, the creator of QLoRA assesses DeepSeek's inference system as on par with OpenAI's stack and better than what Anthropic runs at their scale. Until today, he argues, a production stack at that level existed inside a handful of companies and made their APIs fast and their margins fat; now it is Apache 2.0, runs on both NVIDIA Blackwell and Huawei Ascend, and any startup or university can download and run it. Caveat: "on par with OpenAI" is one expert's assessment relayed on X, not a benchmark result.
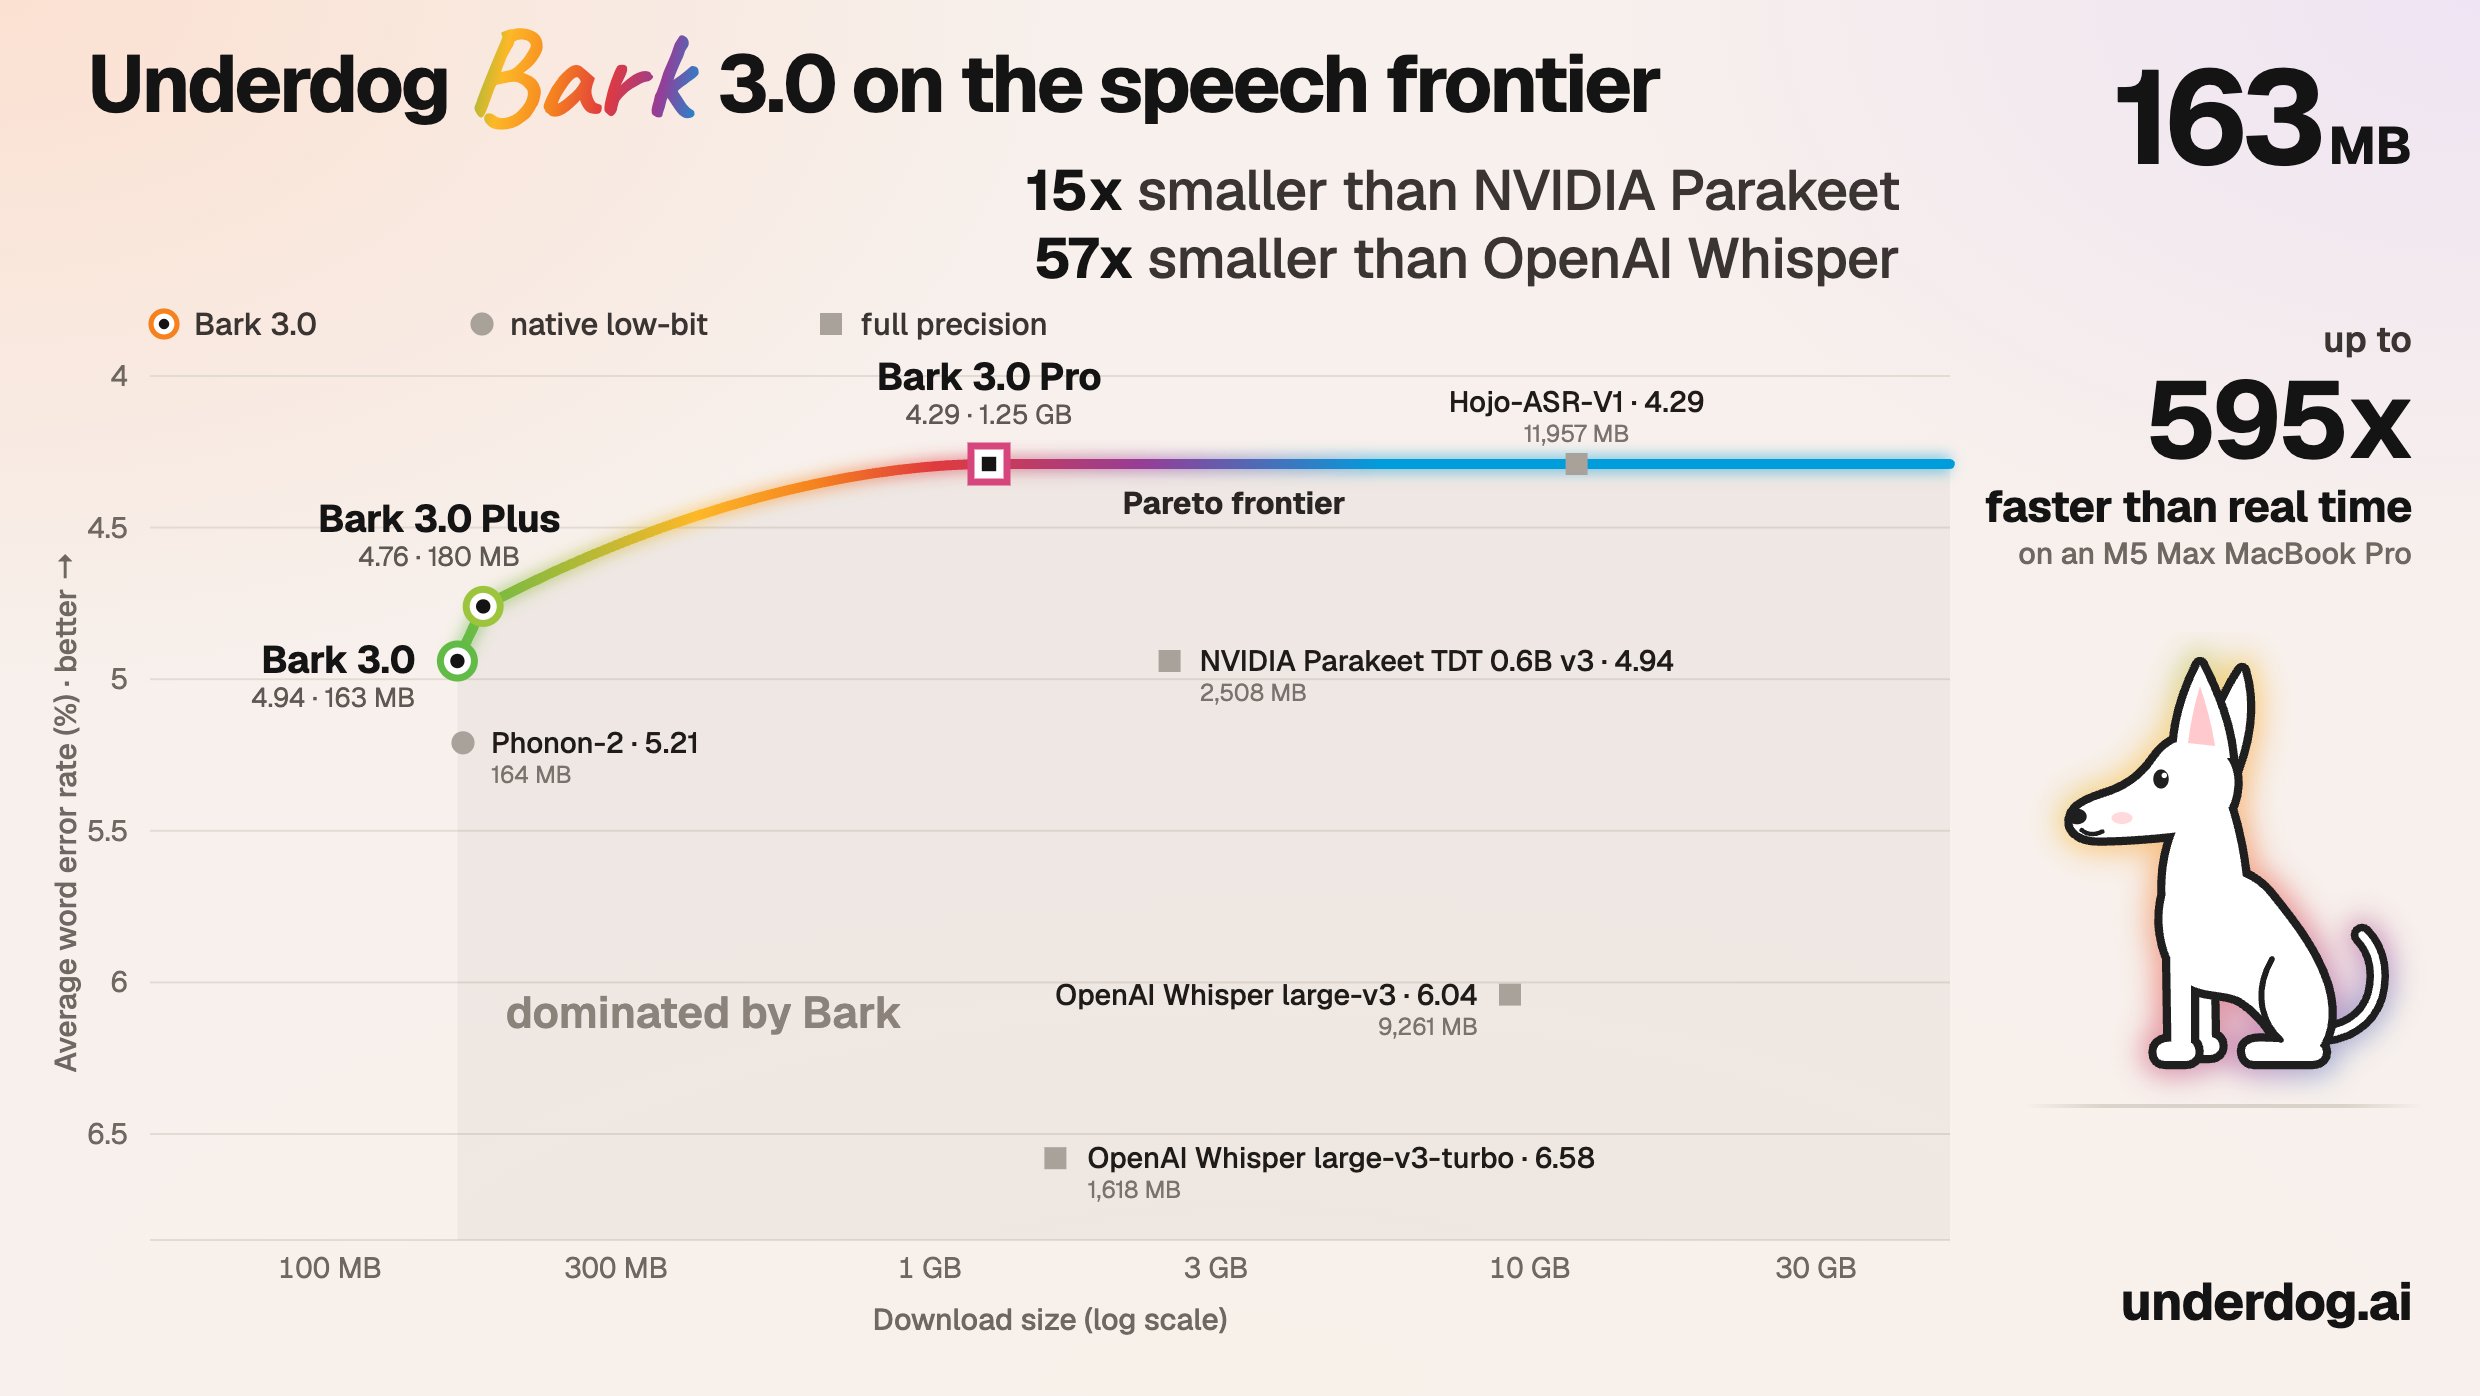
@UnderdogAI released Bark 3.0, claiming a frontier speech model in a 163 MB download: 7.82% word error on the AMI meeting corpus versus 9.42% for NVIDIA's Parakeet (15x larger) and 13.63% for OpenAI's Whisper large-v3 (57x larger), with a minute of audio transcribed in under 0.25 seconds on a MacBook. It runs on laptops and phones for private on-device notes and dictation, under CC-BY 4.0.
@ivanfioravanti highlighted @0xLuigislm's ComfyUI optimization package for Apple Silicon Macs: acceleration confirmed and tested on M5 and newer, with M1-M4 support still theoretical and experimental. He plans to test it on an M5 Max.
Agent Builders Swap Evals, Harnesses, and MCP Launch Playbooks
The practitioner corner traded concrete patterns. @my_knn_totoro reshares @omarsar0's advice to learn building evals, pointing to recommended reading on decision models for evaluation.
@KathrynWang2 recommends @kir_lev's writeup on Ramp's agent platform: after trying existing harnesses, the team built its own cloud-native, model-agnostic version tailored to their infrastructure, and published how.
@vasuman boosts @jdpruettt's pattern for keeping agent memory intact across crashes: run the loop on a boring persistent server, execute code in throwaway Firecracker microVMs, snapshot idle VMs to spin them down, and route interrupts and webhooks to the server so nothing drops while a VM is paused.
On distribution, @DeRonin_ argues ChatGPT apps are the best current channel, claiming agency clients saw +50-200% income on apps they had already shipped, with access to roughly 900M weekly users and no revenue share. His walkthrough covers building the product as an MCP server, writing tool metadata for the model, the plugin submission process, and keeping billing on your own backend via OAuth 2.1. As evidence he cites @skirano's claim of $500K in ARR added in one week from a plugin.
Two culture notes round it out. @thorstenball calls the new Amp episode his most important of the year, with @AmpCode describing a team of 21, one meeting a week, no pull requests, no mandatory code review, and a hundred releases a day. And @kunchenguid recommends following @derekcheng, who says he leads engineering for Jira and Developer AI at Atlassian and will start sharing what the team is building.
Claude Tinkers With Smart Homes and Scorpion Venom
@itsolelehmann's guide to "vibehacking" household devices with Claude Code is making the rounds: open Claude Code on a laptop on your home Wi-Fi, ask it to scan the network and list every device with what could be fixed or controlled, then pick a target. Cited results include AirPlay on a 15-year-old TV, an old Kindle turned family dashboard, and laundry announcements from a washer and dryer; his quoted @nathanclark ended up with a fully custom launcher replacing Samsung Smart Hub. The caveats matter: run it only on your own network and read the commands before approving them.
On the research side, @TMTLongShort highlights @nc_frey, who he notes is Anthropic's head of drug discovery, on Citrini Research using Claude to design binders for scorpion neurotoxins, which kill over 3,000 people a year. Of 211 designs produced and tested, 17 met binder criteria; none bound more than one toxin and none were tested for neutralization. The quote to keep: "Our virtual biologist may have compressed a year's worth of work into a couple days, but biology works at the speed of life."
Practical Takeaway
If you operate internet-facing PHP, today is not a watch-and-wait day: inventory your exposure now, patch the moment the 14:00 UTC release lands, and have a plan to take unpatched apps offline. Pair that with the eMudhra response, updating browsers, OSes, and desktop apps so the blocked certificates actually get blocked on your machines, and audit any ancient devices still attached to your network. If you build with AI, the DeepSeek inference release and the ChatGPT apps launch playbook both reward an hour of hands-on testing this week.
Sources
21 people, a single meeting a week, no quarterly goals, no pull requests, no mandatory code review, no titles (except one dictator), a hundred releases a day, bugs fixed in minutes, famous for killing features. @sqs and @thorstenball on how the Amp team works: https://t.co/BTXBCPAXep
We haven't stopped growing since we launched our new ChatGPT plugin last Tuesday. I've never seen anything like this, we added 500K in ARR this week only! https://t.co/XPy8wxdrEI
Ok so I did the TV hack thing… What started as a very conservative exploration has led to a fully custom home launcher with layouts, backgrounds, material choices and lots of customisation available. I no longer have to deal with Samsung Smart Hub nonsense. It's already live and working but now in a massive refinement pass thats been running while I'm in meetings.
Where do you go next after reporting from the Strait of Hormuz? For the past three months, Citrini Research, an independent research firm, has been working with our team and an internal research model to see if they could use AI to create a new drug. What follows is an entertaining, candid, and humbling account of a group of motivated nonexperts (or “filthy casuals”, as Citrini would say) trying to tackle a real problem in human health with Claude. We landed on scorpion neurotoxins, which kill over 3,000 people a year. Of the 211 designs we produced and tested, 17 met our criteria for a binder. None of the designs bound more than one toxin and none have been tested for neutralizing a toxin. One of my favorite quotes from the piece is: “Our virtual biologist may have compressed a year's worth of work into a couple days, but biology works at the speed of life…Over two days, we watched Claude work through problems at a speed that was difficult to comprehend. For the next two months, we spent much of the time becoming familiar with laboratory turnaround times (This mostly involved sending memes in Slack).”
We at Ramp tried a bunch of agent harnesses and ended up building our own. Cloud-native, model-agnostic, tailored to our infrastructure and product. And we published how we built it: https://t.co/chlSftqDMi
Full details of a remotely exploitable vulnerability in the core engine of *all* PHP versions will be released tomorrow, October 21st. If your organization has internet facing PHP applications then you need to be ready to patch the minute the update is released or *strongly* consider taking the application offline until you can: https://t.co/hpdTOdvSsQ
How to keep agent memory intact when execution environments crash or sleep: Keep the loop itself on a boring persistent server. Run code execution and bash calls in throwaway Firecracker microVMs. When an environment is idle, snapshot the microVM and spin it down. Route interrupts and webhooks directly to the server so nothing drops while the VM is paused.
🚨 MAJOR SECURITY ALERT 8 certificate authority private keys have been compromised. How bad is it? An attacker holding these keys could impersonate ANY website, including banks, exchanges, or Google, and potentially intercept sensitive communications. The good news: Chrome, Firefox and Apple have already taken action to block the compromised certificates. The bad news: Many apps, developer tools and systems may still trust them. What you should do TODAY: Update your browser, OS and phone. Update desktop apps (Slack, Discord, VS Code, etc.) as patches arrive. Avoid untrusted Wi-Fi until your devices are updated. Only install updates from official sources. Ignore any email offering a "certificate fix". This is a serious compromise of internet trust infrastructure, not just another website hack. Full technical details: https://t.co/i5MxKTe8co
I finally released my work, @ComfyUI optimization package tailored for Apple Silicon Macs. Acceleration support is confirmed and tested for M5+, M1-M4 is theoretical and experimental. https://t.co/d10CsCwhUL
Hey everyone, I’m Derek. I lead engineering at Atlassian for Jira and Developer AI. I’ve been a builder most of my career at both startups and big tech. Grew up in Canada but now based in Seattle. I’ll start sharing more of what we’ve got cooking. Would love to connect - DMs are open or feel free to drop a question.
🚨🚨🚨🚨🚨🚨🚨🚨🚨🚨🚨🚨🚨 Reposting this because I think more PS5 jailbreak users should be aware of it. For reasons that are still not fully understood, some jailbroken PS5 consoles can lose proper fan control. The fan may stay at a very low speed (around 19%) even while the console gets much hotter during games. Most users would never notice this unless they monitor temperatures. Possible side effects can include higher APU temperatures, thermal throttling, instability during long gaming sessions, unexpected crashes, or shutdowns related to overheating. This is especially relevant for users who already use ShadowMountPlus, because the new ShadowMountPlusFan release is a modified version of ShadowMountPlus that adds automatic fan-control management. It runs in the background and reapplies the fan settings whenever the PS5 launches a game, exits a game, returns to the home screen, enters rest mode, or wakes up again. The goal is simple: if the fan control gets “stuck,” the plugin restores the settings so the fan can speed up when temperatures rise and slow down again when the console cools down. I’m not posting this to create panic, and it does not mean every jailbroken PS5 is affected. I’m sharing it because many users already use ShadowMountPlus and may not realize that a fan-control issue can occur on some setups. If you use a jailbroken PS5, it is worth checking your temperatures and making sure your fan-control setup is working properly. UPDATE: EDIT: ShadowMountPlus developer Drakmor has released a new fan_target helper that is intended to be used separately alongside the original ShadowMountPlus, not by replacing it with a different fork. It automatically re-applies custom fan targets after game launches, dashboard returns, and rest-mode transitions, which should address the low-fan-speed issue some jailbroken PS5 users experienced. https://t.co/4BndFkxuvA Reddit Post Link Source - https://t.co/EBtUrEekmo
The PHP security team is giving advance notice: Upcoming security release Wed, Oct 21st 2026, 14:00UTC, two critical vulnerabilities, both rated CVSSv4 9.2. PHP users are encouraged to prepare to update. Earlier release if details become public or active exploit evidence.
The guy who gave us QLoRA, says DeepSeek's inference system is on par with OpenAI's stack and better than what Anthropic runs, at least at their scale. Now check the license. Apache 2.0. Until today a production stack at that level existed inside a handful of companies. It was the thing that made their API fast and their margins fat, and none of them ever showed it to anyone. Today any startup, any university, any cloud in any country can download it, read it and run it. It runs on NVIDIA Blackwell and on Huawei Ascend, so it isnt tied to 1 chip vendor either. This is what I mean when I say open weights are about more than downloading a chatbot. DeepSeek is giving away the knowledge that only a few labs had, and that changes who can build an AI company at all. Respect @deepseek_ai
just mitm'd TLS on an iPod Touch 4 without installing a CA cert on it this thing is never getting a security update! just like many IoT devices (if they ship with any global root cas at all...)
I don't really understand why this would happen. It seems higher-effort than standard key generation. https://t.co/FKjFUq68fG